

Introduction
Exploratory API testing helps us go beyond checking whether an API simply meets its documented requirements. It encourages us to understand what could go wrong, where meaningful risks may exist, and what is still unknown.
API requirements tell us what a feature is expected to do. As testers, however, we also need to question those expectations and explore the risks behind them.
This is where test charters become valuable.
In this article, I will share a practical approach to turning API requirements into focused test charters for exploratory API testing, using questions and risks rather than immediately creating test cases.
Start Exploratory API Testing With the Requirement
Imagine a transport management system containing Stops, Timetables, Vehicles, and Operations.
We receive a simple requirement:
Allow an authenticated consumer to retrieve the current details of a stop using its identifier.
The acceptance criteria might cover:
- A valid Stop ID returns the correct stop.
- An unknown Stop ID returns an appropriate error.
- Authentication is required.
- The response follows the API contract.
It would be easy to turn these directly into test cases.
Before doing that, however, there is another useful question to ask:
What risks are hidden behind this requirement?
That question changes how we approach testing.
Test Cases Verify. Test Charters Investigate.
A test case usually verifies something we already know.
For example:
Request an unknown Stop ID and verify that the expected error is returned.
A test charter defines a broader testing mission:
Explore how the Stop API behaves across normal, invalid, and changing stop conditions.
The difference can be summarized simply:
A test case defines what to verify. A test charter defines what to investigate.
A useful charter normally contains:
- Purpose — why we are exploring.
- Focus — which risks or behaviours matter.
- Test Ideas — where the exploration could begin.
Test ideas provide direction without defining every action in advance. This makes the charter particularly useful for exploratory testing, where new information can influence what we choose to investigate next.
Turn API Requirements Into Questions
Before writing charters, we need questions.
One simple questioning model I use in exploratory API testing is:
EXPECTED → NEGATIVE → EDGE → INTERACTION → UNKNOWN
This is not a formal methodology. It is simply a practical way to think beyond acceptance criteria.
Expected
Start with what should normally happen.
Does the API return the correct Stop? Is the current state accurate? Does the response follow the contract?
This gives us a baseline.
Negative
Challenge the assumptions behind the requirement.
What happens with an unknown or malformed identifier? What happens without authentication? Are errors handled consistently?
The goal is not simply to send random invalid inputs.
Ask:
What assumption is the API making, and what happens when that assumption is violated?
Edge
Look for boundaries, especially business boundaries.
A Stop may move through different lifecycle states:
PLANNED → ACTIVE → TEMPORARILY_CLOSED → INACTIVEWhat happens during a state transition? What happens exactly at an activation boundary? How are incomplete or unusual Stop states represented?
These questions often reveal risks that are not obvious from the API contract alone.
Interaction
A Stop rarely exists in isolation.
             STOP
              │
       ┌──────┼──────┐
       ▼      ▼      ▼
  TIMETABLE SERVICE OPERATIONS
If an operational change temporarily closes a Stop, does related timetable information reflect that change consistently?
We do not necessarily need to test every connected service in the same session.
The interaction simply helps us discover another potential risk.
Unknown
Some questions cannot be predicted during test preparation.
Suppose repeated requests after a Stop state change return inconsistent information.
That observation creates a new question, which creates a hypothesis, which leads to another test.
OBSERVE
   ↓
QUESTION
   ↓
HYPOTHESIS
   ↓
EXPLORE
   ↓
LEARN
   └──────→ NEW QUESTION
This feedback loop is an important part of exploratory API testing: what we learn during execution influences what we explore next.
Turn Questions Into Testing Risks
After asking these questions, we can group them into meaningful risk areas.
| Risk Area | What Are We Exploring? |
|---|---|
| Functional | Does the feature behave according to its business rules? |
| Negative | How does it handle invalid or unexpected conditions? |
| Authorization | Is access controlled correctly? |
| Data Integrity | Is information accurate and consistent? |
| Interaction | Are changes reflected correctly across related areas? |
| Performance | Does the API remain responsive and stable? |
This is the key step.
We are no longer asking:
How many test cases can I create from this requirement?
Instead, we are asking:
Which risks deserve focused exploration?
This keeps the testing effort focused on meaningful behaviour rather than simply maximizing test-case coverage.
Turn Risks Into Focused Test Charters
Not every risk needs its own charter.
A charter should be separated when a risk is important enough to deserve a focused testing mission.
For example:
| Charter | Purpose |
|---|---|
| Functional & Lifecycle | Explore Stop behaviour across normal and changing lifecycle states. |
| Negative & Error Handling | Explore behaviour under invalid and unexpected conditions. |
| Authorization | Explore access behaviour under different authorization conditions. |
| Data Integrity | Explore whether Stop information remains accurate and consistent after changes. |
| Cross-Domain Interaction | Explore consistency between Stop, Timetable, and operational information. |
| Performance & Stability | Explore responsiveness and stability during expected usage. |
These are examples, not a mandatory checklist.
A simple feature might need only two charters. A feature with complex state transitions may need a dedicated lifecycle charter. A change affecting multiple services may justify a cross-domain charter.
The principle is:
Split test charters by meaningful risk, not by a fixed formula.
A Practical Exploratory API Testing Charter
Once the risk is clear, the charter itself can remain concise.
Functional & Lifecycle Charter
Purpose
Explore how Stop information behaves across normal and changing lifecycle states.
Focus
- Stop information
- Lifecycle states
- State transitions
- Response consistency
Test Ideas
- Explore Stops in different lifecycle states.
- Observe behaviour around state transitions.
- Compare information before and after a state change.
- Look for unexpected or inconsistent behaviour.
- Follow interesting observations with further exploration.
Notice that the charter does not prescribe every request or expected result.
It gives the tester a mission and enough direction to begin.
That distinction is important. A charter should support exploration, not quietly become another scripted test case.
A Simple Exploratory API Testing Flow
The overall process can be summarized as:
REQUIREMENT
     ↓
ASK QUESTIONS
     ↓
IDENTIFY RISKS
     ↓
GROUP RISKS
     ↓
CREATE FOCUSED CHARTERS
     ↓
EXPLORE
     ↓
LEARN
Acceptance criteria provide the starting point.
Negative and edge thinking challenge expected behaviour. Interactions reveal risks outside the immediate endpoint. Unexpected observations create new questions during execution.
Test charters bring those ideas together into focused exploratory missions.
Or more simply:
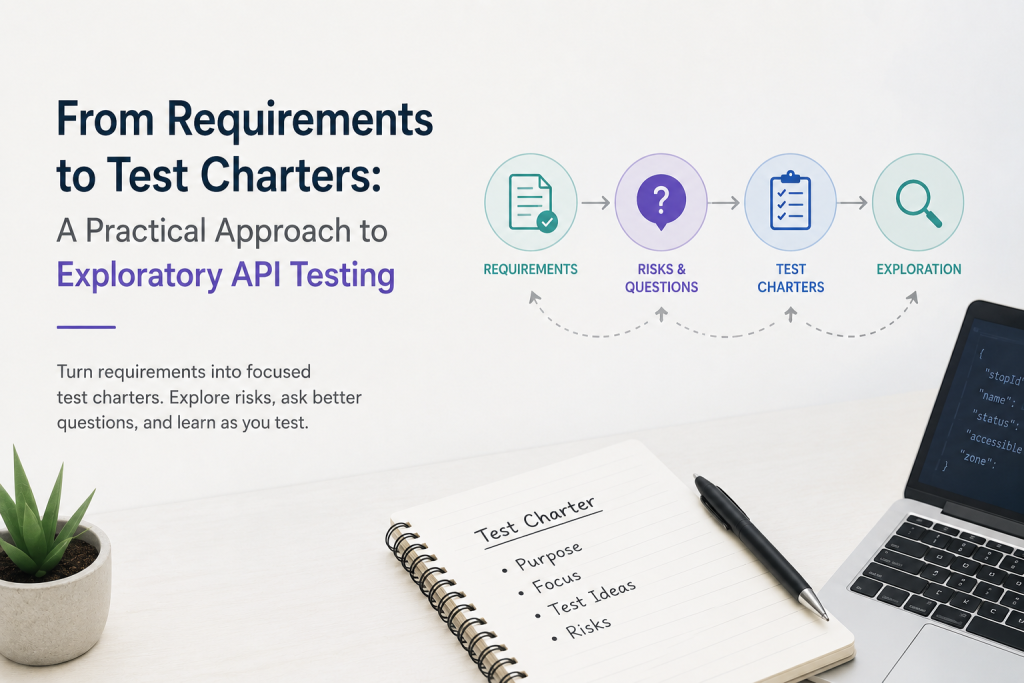
Requirement → Questions → Risks → Focused Charters → Exploration → Learning
Final Thoughts
Turning requirements into test charters is not about rewriting acceptance criteria in another format.
It is about moving from:
“What should I verify?”
to:
“What is worth investigating?”
In exploratory API testing, a requirement can reveal functional, negative, authorization, data integrity, interaction, or performance risks. Not every risk needs a separate charter.
The tester’s job is to identify which risks matter enough to deserve focused exploration and then use what is learned during testing to decide where to explore next.
The most useful flow to remember is:
Requirement → Questions → Risks → Focused Charters → Exploration → Learning
And perhaps the most important principle is:
A good test charter gives enough direction to start exploring, but enough freedom to follow what you discover.
References & Further Reading
Cem Kaner — Defining Exploratory Testing
A useful foundation for understanding exploratory testing as an approach where learning, test design, execution, and interpretation support each other throughout the testing process.
Defining Exploratory Testing – Cem Kaner
ISTQB — Certified Tester Foundation Level Syllabus v4.0.1
See the Exploratory Testing section for additional background on exploratory testing and the use of test charters to guide testing sessions.